

If you are searching for the top 12 best SOC 2 vendors with monthly pricing plans, you have landed in exactly the right place. In today’s hyper-competitive SaaS landscape, SOC 2 compliance is no longer optional — it is the baseline standard that enterprise buyers, investors, and partners require before signing any contract. In fact, a growing number of Fortune 500 procurement teams now reject vendors outright if they cannot produce a current SOC 2 report. As a result, the pressure on cloud-based companies to achieve and maintain certification has never been higher.
Fortunately, the compliance automation market has matured significantly. Rather than spending six to twelve months manually gathering evidence, writing policies, and coordinating with auditors, organizations can now leverage purpose-built platforms that automate up to 90% of the entire process.
That said, choosing the right SOC 2 vendor is not a straightforward decision. Each platform serves a different stage of business, budget range, and compliance maturity level. For instance, a seed-stage startup pursuing its first Type I report has fundamentally different needs than a mid-market SaaS company managing SOC 2, ISO 27001, and HIPAA simultaneously. Similarly, an enterprise with a 200-person engineering team needs deeper CI/CD integration and GRC consolidation than a ten-person startup does.
To help you cut through the noise, this article breaks down the 12 best SOC 2 compliance vendors with monthly pricing plans. For each vendor, you will find a detailed overview, a full breakdown of key features, an honest assessment of pros and cons, and transparent monthly pricing plans. So you can compare your options side by side and make a confident, well-informed investment decision.
Top 12 Best SOC 2 Vendors with Monthly Pricing Plans
1. Vanta

Vanta leads the compliance automation market with approximately 35% market share, and it actively empowers over 14,000 businesses to achieve and maintain SOC 2 certification. Furthermore, the platform connects to more than 400 integrations, including AWS, GitHub, Okta, and Google Workspace, automatically pulling around 85% of audit evidence without manual effort. Consequently, organizations that previously spent months preparing for audits now complete the process in weeks. Moreover, Vanta continuously monitors controls in real time, alerting teams instantly when a security misconfiguration appears or an MFA setting changes.
Features
- Automated evidence collection from 400+ integrations including AWS, Azure, GitHub, and Okta
- Over 1,200 automated security tests with real-time control monitoring and instant alerts
- Policy library with 200+ ready-to-use, customizable templates for audit-ready documentation
- Public-facing Trust Center to showcase security posture to prospects and customers
- Vendor risk management with automated security questionnaire workflows
- Employee security training with completion tracking and automated reminders
Pros
- Industry-leading integration library with 400+ native connections
- Intuitive interface that non-technical teams can navigate without steep learning curves
- Continuous monitoring reduces audit prep from months to weeks
- Strong customer success support with dedicated onboarding assistance
Cons
- Pricing can be high for very early-stage startups with limited budgets
- Add-ons such as advanced questionnaire automation and Trust Center branding increase total costs
Pricing
- Starter: $833
- Growth: $1,250
- Scale: $2,083
- Enterprise: Custom
2. Drata
The platform functions as a true AI-native trust management system, meaning it actively automates 90% or more of controls across cloud environments, code repositories, and identity systems. Beyond basic compliance, Drata also centralizes governance, risk, and compliance in one unified system through its GRC module. Furthermore, its Audit Hub keeps engineers and auditors collaborating in a shared workspace, dramatically reducing back-and-forth during the audit observation period. Teams using Drata particularly appreciate how deeply it integrates with CI/CD pipelines and developer tooling, treating compliance as a natural extension of the engineering workflow rather than a separate burden.
Features
- Real-time control monitoring with automated alerts for failed tests and security drift
- Vendor risk management with automated questionnaires, scoring, and ongoing monitoring
- Custom framework builder for organizations with proprietary or niche compliance requirements
- Access review automation with scheduling, approval workflows, and remediation tracking
Pros
- Deepest developer-friendly automation with CI/CD and code repository integrations
- Audit Hub significantly reduces auditor coordination time and evidence request cycles
- AI capabilities genuinely reduce manual compliance review effort across the team
- Strong multi-framework mapping ensures controls transfer across certifications without duplication
Cons
- Initial setup can be complex given the platform’s extensive features and configuration options
- Some advanced modules and add-ons carry additional costs beyond the base subscription
Pricing
- Startup: $625
- Business:$1,458
- Scale: $2,833
- Enterprise: Custom
3. Secureframe
Furthermore, the platform was architected by former auditors and compliance experts, which means the workflows mirror exactly what auditors expect to see. As a result, teams navigating their first SOC 2 audit find Secureframe particularly reassuring because it breaks down each requirement into guided, checklist-style steps that eliminate guesswork. Additionally, Secureframe supports more than 25 frameworks—including SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, CCPA, and FedRAMP readiness—making it an excellent long-term compliance platform as organizations mature. Moreover, its AI-powered policy builder provides text revision tools and automated version control, enabling even small teams without dedicated legal staff to maintain audit-ready documentation.
Features
- Guided, plug-and-play compliance workflows designed by former auditors for first-time users
- Automated evidence collection integrated with cloud infrastructure, identity, and ticketing tools
- AI-powered policy builder with text revisions, version control, and automated framework updates
- Cross-framework control mapping to reduce duplicate work across multiple certifications
Pros
- Guided workflows make compliance accessible for founders without security backgrounds
- Former auditor involvement in platform design ensures controls align with real audit expectations
- Strong AI policy automation reduces time spent on documentation from days to hours
Cons
- Some users have reported occasional bugs in integration syncing that require manual retries
- Advanced GRC capabilities are less deep compared to platforms like Drata for technical teams
Pricing
- Starter::$625
- Growth:$1,042
- Scale: $1,667
- Enterprise: Custom
4. Sprinto
Sprinto approaches SOC 2 compliance differently from most competitors by delivering a highly adaptive, AI-native platform that continuously adjusts to each organization’s specific risk profile and system architecture. Moreover, the platform currently holds approximately 10% of the compliance automation market and actively serves companies across the US, Europe, and Asia-Pacific with equal effectiveness. Consequently, Sprinto has earned a reputation as one of the most cost-effective compliance automation tools available, particularly for teams that want a transparent, all-inclusive pricing structure with no surprise add-on fees. Furthermore, the platform uses programmable monitoring rules and role-based dashboards that allow compliance owners, security engineers, and executive stakeholders each to see the information most relevant to their role
Features
- Adaptive automation with an intelligent control framework that adjusts to business needs automatically
- Infinite Frameworks feature: AI-powered mapping allows onboarding of any custom framework in one day
- Supports 200+ compliance frameworks out of the box, including all major standards
- Programmable monitoring rules with role-specific dashboards for different stakeholder types
Pros
- Most cost-effective all-inclusive pricing among major compliance automation platforms
- Infinite Frameworks’ feature uniquely addresses custom and niche compliance requirements
- No hidden add-on fees makes total cost of ownership highly predictable
Cons
- As a newer platform (founded in 2020), some users report occasional bugs that require workarounds
- Integration library is smaller than Vanta’s or Drata’s, which can create gaps in evidence collection
Pricing
- Startup: $333/month
- Growth: $583/month
- Scale: $833/month
- Enterprise: Custom
5. Thoropass
Thoropass solves one of the most frustrating problems in compliance by combining automation software and audit services under a single roof, eliminating the coordination overhead that companies face when managing a separate CPA firm. Additionally, the platform assigns in-house auditors directly within the compliance workspace, so teams handle evidence collection, continuous monitoring, and the actual audit itself without switching between systems or vendors. The platform supports 19 compliance frameworks, including SOC 2, ISO 27001, HIPAA, GDPR, CCPA, PCI DSS, and HITRUST, making it versatile enough for companies with complex regulatory requirements. Thoropass uses an AI-powered First Pass evidence review, which checks submitted evidence before auditors ever see it, dramatically reducing revision cycles and observation period delays.
Features
- Connected audit model with in-platform auditors, eliminating the need for a separate CPA firm
- AI-powered First Pass evidence review that checks submissions before auditors see them
- Automated evidence collection with continuous monitoring across cloud and identity systems
- Built-in Risk Register for proactive gap identification and remediation tracking
Pros
- Unique single-vendor model for both compliance software and audit services reduces coordination friction
- In-platform auditors provide faster, more transparent audit timelines than managing separate CPA firms
- First Pass AI review reduces evidence revision cycles and shortens observation periods
Cons
- Integration options are more limited compared to Vanta and Drata, creating gaps for complex stacks
- Bundled pricing with audit services can appear higher than software-only platforms at first glance
Pricing
- Starter: $833/month
- Growth: $1,667/month
- Scale: $2,500/month
- Enterprise: Custom
6. Hyperproof

Hyperproof actively fills a critical gap in the compliance market by providing a platform specifically designed for organizations managing three or more compliance frameworks simultaneously, and it does so with elegance and precision. Additionally, Hyperproof supports more than 118 frameworks with over 70 integrations, giving it the broadest framework library of any compliance automation platform currently available. Moreover, the platform connects controls to risks in a centralized data model, meaning teams can trace every control back to a specific risk and every risk forward to the frameworks that address it. Consequently, organizations that previously struggled to maintain visibility across multiple certifications find Hyperproof transformative. It is particularly well-suited to mid-market and enterprise organizations where compliance programs span multiple business units, regions, and regulatory environments.
Features
- Supports 118+ compliance frameworks—the largest library of any major compliance automation platform
- Centralized control data model connecting controls to risks and frameworks in a single source of truth
- Automated workflows for control testing, evidence collection, and audit readiness reporting
- Multi-business-unit control mapping for organizations with distributed compliance programs
Pros
- Excellent for mid-market and enterprise organizations managing compliance across multiple business units
- Strong customer support consistently recognized in analyst reports and user reviews
- Control-to-risk linkage provides deeper GRC visibility than most compliance automation tools
Cons
- Continuous monitoring posture can be challenging to maintain seamlessly compared to Vanta or Drata
- Customization options are more limited than some enterprise GRC platforms for complex environments
Pricing
- Essential: $1,000/month
- Professional: $1,667/month
- Business: $2,500/month
- Enterprise: Custom
7. AuditBoard

AuditBoard stands as the definitive enterprise GRC platform in the compliance automation market, and it currently serves approximately half of the Fortune 500—a remarkable market penetration that speaks to its depth and reliability. Furthermore, the platform consolidates audit, risk, and compliance functions into a single AI-powered system that connects people, processes, and data across entire organizations. Moreover, its CrossComply module specifically handles multi-framework SOC 2 and cybersecurity compliance, while SOXHUB manages financial controls, and RiskOversight addresses enterprise risk management. Additionally, AuditBoard’s AI-powered workflows automate routine audit tasks—document requests, stakeholder tracking, remediation projects—giving compliance teams the capacity to focus on strategic risk decisions rather than administrative work. Consequently, large enterprises managing complex audits across multiple teams, geographies, and business units find AuditBoard uniquely capable of handling the scale and sophistication their programs demand.
Features
- CrossComply module for multi-framework compliance including SOC 2, ISO 27001, NIST, CMMC, PCI DSS
- SOXHUB module for SOX management with integrated financial control testing and reporting
- RiskOversight module connecting enterprise risk management to compliance and audit activities
- AI-powered workflow automation for document requests, stakeholder tracking, and remediation
Pros
- Most comprehensive GRC consolidation available, connecting audit, risk, and compliance in one system
- AI automation handles routine tasks at a scale that manual processes or smaller platforms cannot match
- Unified data model eliminates the fragmentation of managing separate audit and compliance tools
Cons
- Implementation requires significant time and often involves a dedicated internal compliance team
- Complexity of features may overwhelm organizations without experienced GRC professionals on staff
Pricing
- CrossComply: $ 4,167/month
- GRC Suite: $6,250/month
- Full Platform: $8,333/month
- Enterprise: Custom
8. OneTrust
OneTrust operates at a different level of sophistication than most compliance automation tools, and it actively serves global enterprises that need to manage privacy, data governance, and security compliance as an integrated system rather than as separate programs. Furthermore, OneTrust acquired Tugboat Logic in 2021 specifically to strengthen its risk and compliance capabilities, particularly in automating information security assurance and SOC 2 audit readiness. Consequently, the platform today uniquely bridges the gap between privacy regulations like GDPR and CCPA and security frameworks like SOC 2, enabling teams to manage both from a centralized GRC environment. Moreover, OneTrust’s consent management, data mapping, and privacy impact assessment capabilities are unmatched in the compliance automation space, making it the clear choice for organizations where privacy is a core strategic priority.
Features
- Privacy impact assessments (PIAs) and data protection impact assessments (DPIAs) are built in
- Automated vendor risk assessment with third-party due diligence workflows and scoring
- Regulatory change monitoring that automatically updates compliance programs with new requirements
- Security questionnaire automation with AI-assisted responses for faster enterprise deal closure
- Audit readiness dashboard with real-time control status and gap identification
Pros
- Best-in-class privacy management capabilities that no other compliance automation platform matches
- Uniquely bridges privacy regulations and security frameworks in one integrated platform
- Global regulatory coverage is the most comprehensive available for multinational enterprises
Cons
- Platform complexity can require dedicated compliance staff with privacy and security expertise
- Not the most efficient choice for organizations that only need SOC 2 without privacy program needs
Pricing
- Privacy Essentials: $2,083/month
- Security & Compliance: $3,125/month
- Enterprise GRC: $4,167/month
- Enterprise: Custom
9. Scytale
Scytale has quickly established itself as one of the most innovative compliance automation platforms, and it actively combines AI-powered automation with hands-on guidance from dedicated GRC specialists assigned to each account. Furthermore, the platform’s AI compliance agent—named Scy—acts as a persistent co-pilot that evaluates evidence, flags risks, and guides organizations toward continuous audit readiness without requiring constant human intervention. Moreover, Scytale earned Leader status in GRC, Security Compliance, and Cloud Security in the G2 Fall 2025 Report, along with recognition as Fastest Implementation and Best Relationship across multiple regions, affirming that its efficient onboarding model delivers results quickly. Additionally, Scytale supports over 40 security and privacy frameworks and includes capabilities for penetration testing management, AI-generated security questionnaire responses, and automated Trust Center communications.
Features
- AI-generated security questionnaire responses to accelerate enterprise sales deal closure
- Automated Trust Center communications for real-time security posture sharing with customers
- Penetration testing management with evidence tracking and remediation workflows
- User access reviews with Okta SSO integration and user list imports from critical systems
Pros
- Dedicated GRC specialist per account provides unmatched personalized compliance guidance
- Scy AI agent delivers genuine intelligence beyond basic task automation
- G2 recognition for Fastest Implementation confirms quick time-to-value for new customers
Cons
- As a newer company, the integration ecosystem is still growing compared to established competitors
- Some customization options may be insufficient for organizations with highly specific compliance needs
Pricing
- Starter: $667/month
- Growth: $1,083/month
- Scale: $1,667/month
- Enterprise: Custom
10. LogicGate
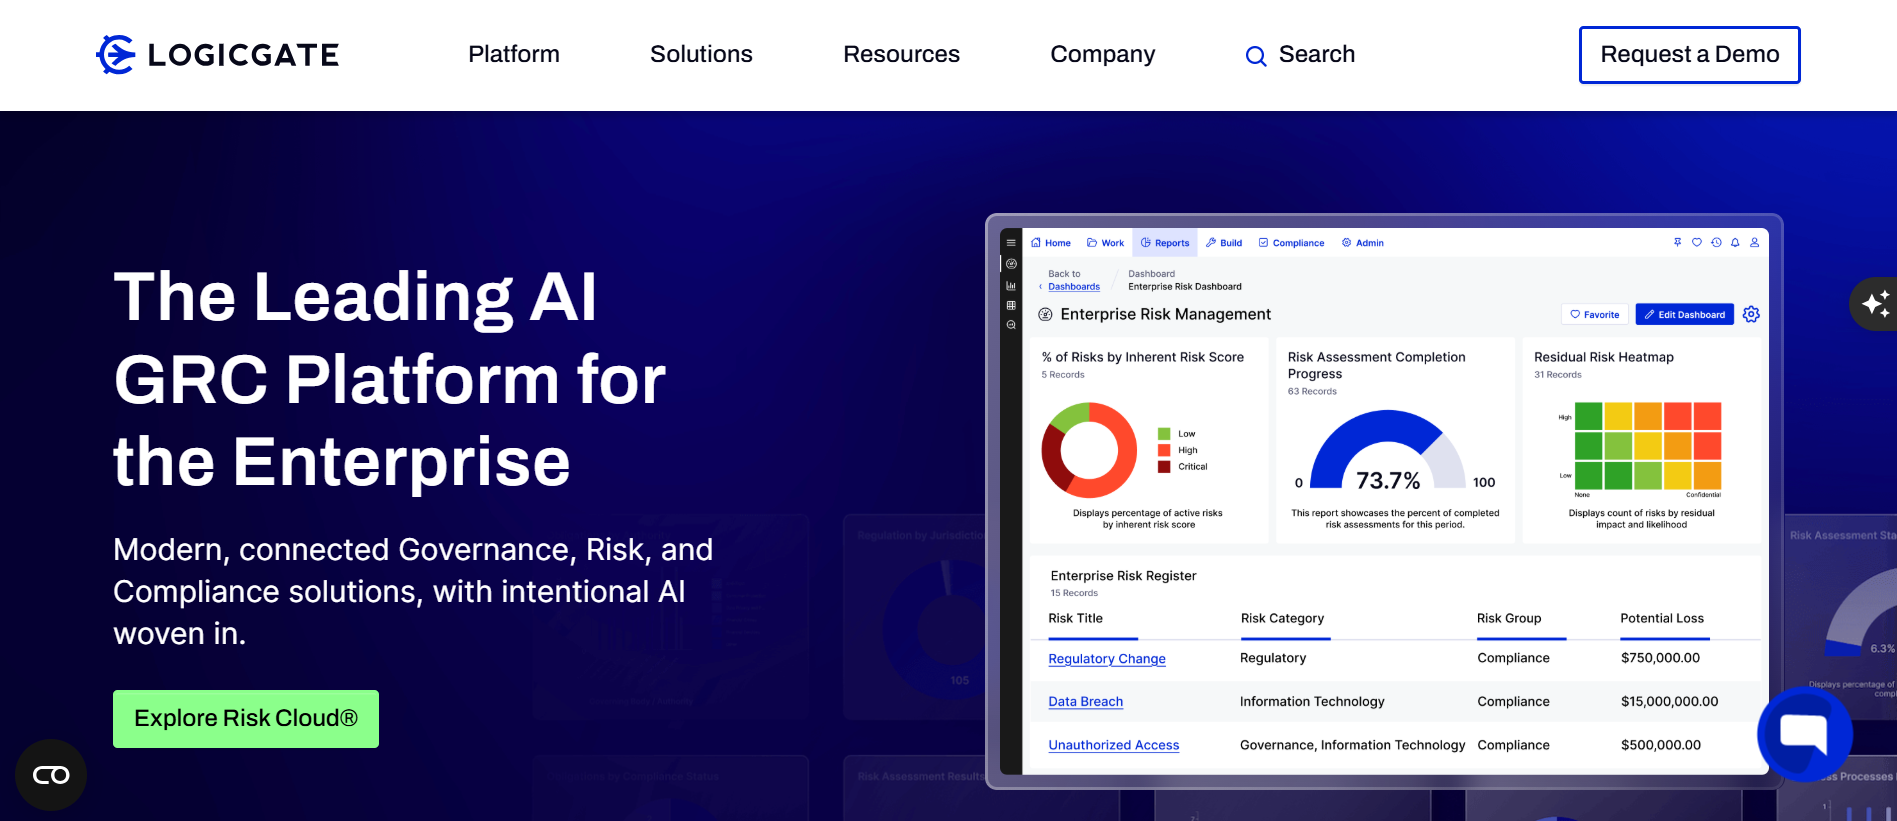
LogicGate Risk Cloud takes a fundamentally different approach to compliance automation by providing a no-code platform that allows organizations to build, customize, and manage their own risk and compliance workflows without requiring engineering resources. Furthermore, the platform has recently revamped its risk and compliance capabilities with an emphasis on operational resilience, and its enhanced vendor risk management module now includes continuous monitoring alongside traditional assessment workflows. Additionally, LogicGate is modular by design, meaning organizations pay only for the specific risk and compliance modules they need rather than purchasing a fixed bundle with features they may never use. Moreover, the platform enables compliance teams to design their own process flows, approval chains, and data collection forms, making it uniquely adaptable to organizations with unusual operational structures or industry-specific requirements.
Features
- Modular architecture allows organizations to purchase only the risk/compliance modules they need
- Enhanced vendor risk management module with continuous monitoring and automated assessment
- Flexible approval chains and data collection forms are adaptable to unique organizational structures
- SOC 2, ISO 27001, NIST, CMMC, PCI DSS, and other frameworks support with control mapping
- Risk identification, assessment, scoring, and tracking from a single centralized dashboard
Pros
- Maximum workflow flexibility through a no-code builder allows compliance programs to match operational reality
- Modular pricing means organizations never pay for compliance features they do not actively use
- Well-suited for compliance teams with in-house GRC expertise who want full program control
Cons
- Setup and configuration are significantly more time-intensive than guided platforms like Secureframe
- Not ideal for first-time compliance teams without prior GRC program experience
Pricing
- Essential: $1,250/month
- Professional: $2,083/month
- Advanced: $3,333/month
11. Scrut Automation
Scrut Automation actively distinguishes itself from the competition through a risk-first compliance philosophy that begins every program by understanding an organization’s unique risk landscape before mapping controls to frameworks. Furthermore, the platform was purpose-built for startups and mid-sized SaaS companies that want to achieve SOC 2 and ISO 27001 compliance efficiently without the cost and complexity of enterprise GRC tools. Additionally, Scrut uses its Harmony AI engine for automated framework crosswalking, meaning that controls implemented for SOC 2 automatically map across ISO 27001, HIPAA, PCI DSS, and 25+ other frameworks, eliminating duplicated effort. Moreover, the platform provides real-time insights into regulatory standing through its automated security posture tracking, and many users specifically praise the clarity and intuitiveness of Scrut’s dashboards for compliance status visibility.
Features
- Risk-first compliance approach that maps controls to frameworks based on organizational risk profile
- Harmony AI engine for automated framework crosswalking across 25+ compliance standards
- Pre-built library of 50+ compliance policies for rapid compliance foundation establishment
- Trust Vault for secure sharing of audit evidence and compliance posture with prospects
- Real-time security posture tracking with automated insights into regulatory standing
Pros
- Risk-first compliance approach that maps controls to frameworks based on organizational risk profile
- Harmony AI engine for automated framework crosswalking across 25+ compliance standards
- Pre-built library of 50+ compliance policies for rapid compliance foundation establishment
- Trust Vault for secure sharing of audit evidence and compliance posture with prospects
- Real-time security posture tracking with automated insights into regulatory standing
Pros
- Risk-first approach produces more targeted, efficient compliance programs than checklist-driven tools
- Harmony AI crosswalking is among the most effective automated framework mapping available
Cons
- Does not bundle audit services, meaning organizations must coordinate separately with a CPA firm
- Some users experience a learning curve when first engaging with advanced platform features
Pricing
- Starter: $1,000/month
- Growth: $1, 458/month
- Scale: $2,083/month
12. Qualys VMDR
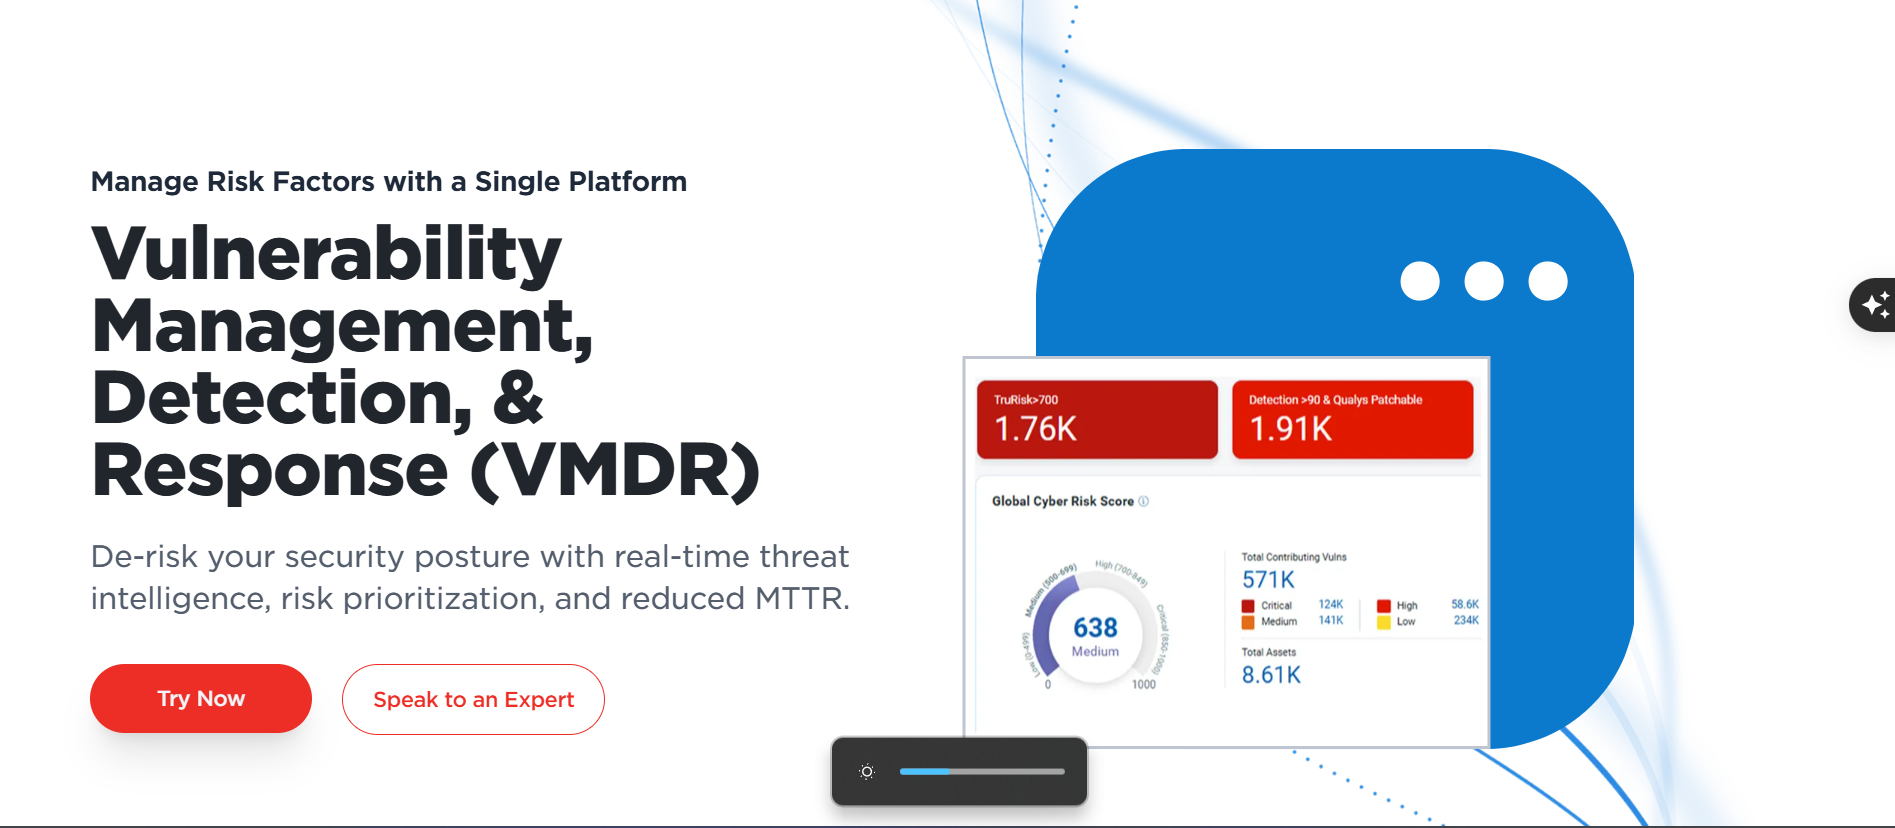
Qualys takes a distinctly security-first approach to SOC 2 compliance by building compliance management directly on top of an enterprise-grade vulnerability management and asset discovery engine, creating a platform where security posture and compliance readiness are genuinely unified rather than loosely connected. Furthermore, Qualys VMDR (Vulnerability Management, Detection, and Response) uses machine learning-enhanced asset discovery to maintain accurate, real-time inventory across cloud, on-premises, and hybrid environments—a capability that most compliance-only platforms cannot replicate. Consequently, organizations in highly regulated industries where security and compliance teams work closely find Qualys uniquely capable of eliminating the gap between technical security controls and audit-ready documentation.
Features
- ML-enhanced asset discovery providing accurate, real-time inventory across cloud, on-premises, and hybrid environments
- Unified vulnerability management and compliance monitoring in a single platform
- Continuous vulnerability scanning with automated prioritization based on exploitability and business impact
- Multi-framework compliance reporting generating SOC 2, PCI DSS, HIPAA, and NIST from one data source
Pros
- Industry-leading vulnerability management engine provides genuine security depth beyond compliance checkbox work
- ML-driven asset discovery is the most accurate and comprehensive available for complex environments
- Unified platform eliminates the need for separate security and compliance tools for mature organizations
Cons
- Platform depth and complexity require experienced security professionals to configure and operate effectively
- Less suited for startups or companies without an existing security operations function
Pricing
- VDMR Essentials: $833/month
- VDMR Compliance: $1,667/month
- VDMR Cybersecurity: $2,917/month
- Enterprise: Custom
Conclusion
Achieving SOC 2 compliance no longer requires a team of consultants, months of manual effort, or an enterprise-sized budget. As this guide has shown, the best SOC 2 vendors with monthly pricing plans now span a wide range of price points and capability levels — from lean, startup-friendly platforms like Sprinto starting around $333/month, to enterprise GRC powerhouses like AuditBoard designed for Fortune 500 complexity.
Ultimately, the right platform depends on three core factors: your current compliance maturity, the number of frameworks you need to manage, and how many internal resources you can dedicate to the program.