Getting SOC 2 certified once required twelve to eighteen months filled with spreadsheets, urgent evidence collection, and constant email exchanges with auditors. However, the process looks very different today. The best SOC 2 companies for fast certification now shorten that timeline to a few weeks, and in some cases just days for Type I audits. They achieve this shift through AI-driven automation, continuous control monitoring, and close coordination with audit partners.
If a deal depends on your SOC 2 report, then choosing the right provider can directly influence how quickly revenue moves forward. Therefore, selecting a partner becomes a strategic decision rather than a technical one. This guide reviews the top 12 SOC 2 companies for fast certification available in 2026, while also explaining how each option supports speed, efficiency, and audit readiness.
Whether you run a seed-stage SaaS startup pursuing your first enterprise contract or manage a growing mid-market company handling multiple frameworks at once, you will find a provider that fits your timeline and compliance goals.
Top 12 SOC 2 Companies for Fast Certification
1. Comp AI
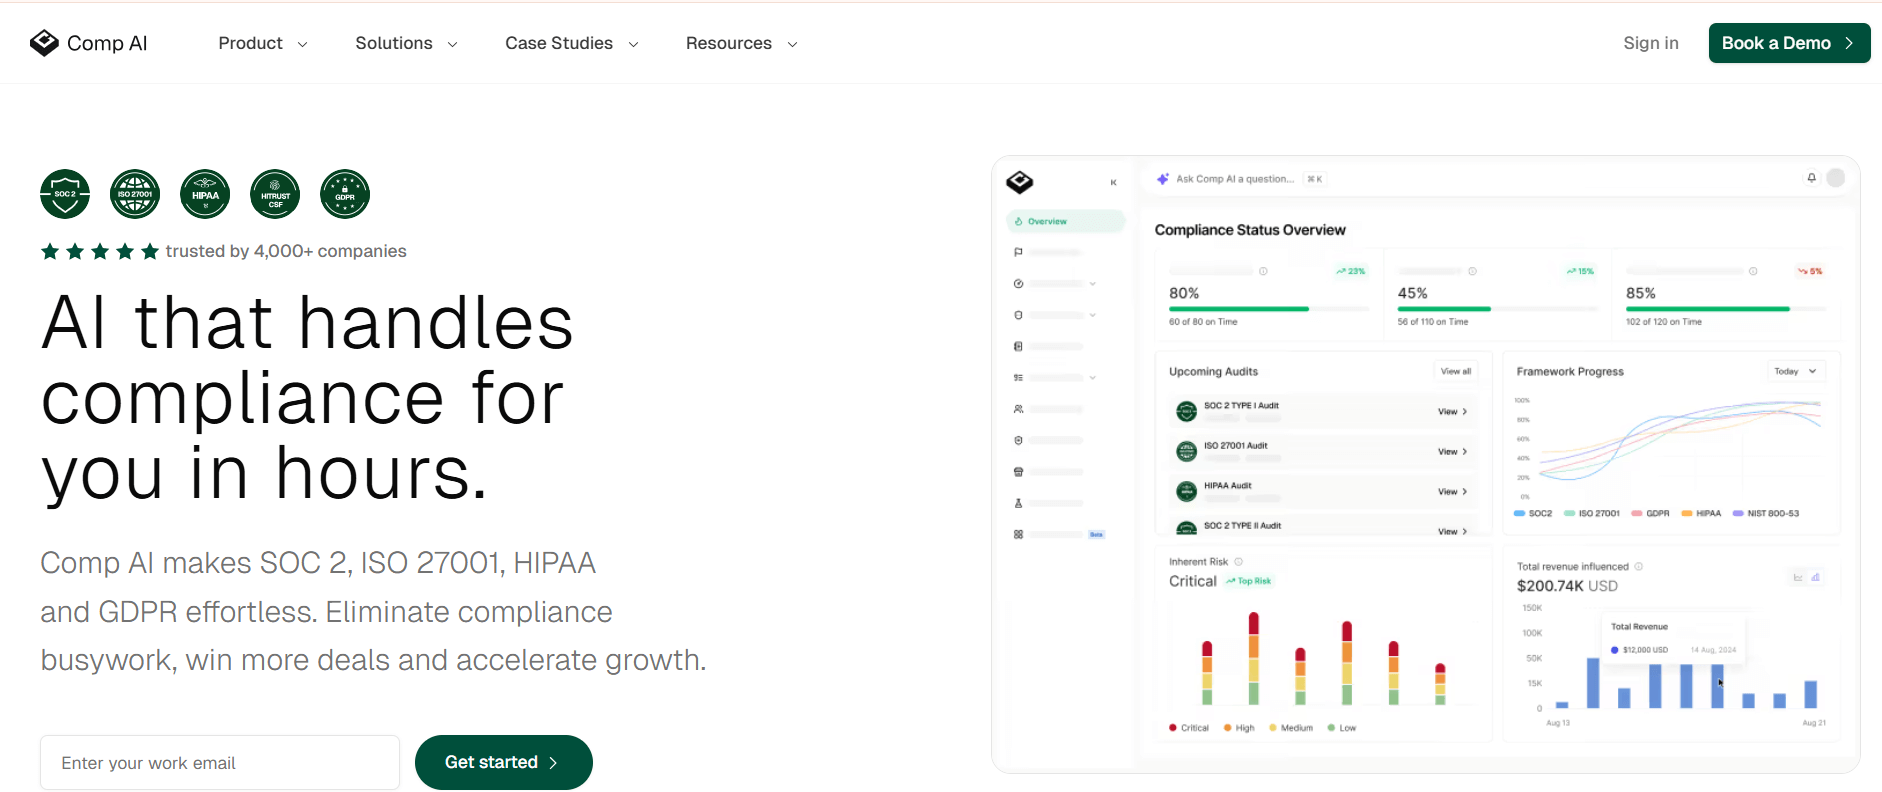
This platform focuses on speed, automation, and clarity, especially for startups that want to reach SOC 2 readiness without heavy manual work. It uses agent-based AI to collect evidence from the start, while it also builds policies and maps controls across multiple frameworks at the same time. In addition, the system includes audit and penetration testing within the package, so teams avoid managing separate vendors. Therefore, companies move faster through compliance tasks, while they maintain clear visibility into their security posture.
Features
- Agent-based AI evidence collection that begins automatically from day one
- AI-generated policy library with more than 100 prebuilt templates
- Automated risk assessment engine that evaluates and prioritizes risks
- Control mapping across 25+ frameworks at the same time
- Open-source codebase that supports self-hosting or cloud deployment
- SOC 2 audit included without a separate CPA fee.
Timeline
- SOC 2 Type I: Audit-ready in 24 hours.
- SOC 2 Type II: Audit-ready in 14 days.
Pricing
• Typically falls between $5,000 and $15,000 or more for platform services, depending on scope and company needs
Pros
- Real-time monitoring keeps teams aware of compliance status at all times
- Fast path to audit readiness compared to traditional approaches
- AI handles repetitive compliance tasks, which reduces manual effort
- Bundled audit and testing remove the need for multiple vendors
Cons
- Requires Slack for full support experience
- Advanced capabilities may feel overwhelming for beginners
Best For
Early-stage SaaS startups, bootstrapped teams, and AI-focused builders that want the fastest and most cost-transparent path to SOC 2 without manual evidence collection.
2. Vanta

Vanta controls a large share of the compliance automation market and many companies recognize it as a leading option for fast SOC 2 certification. It runs more than 1,200 automated hourly control tests across over 3oo integrations, which allows teams to monitor systems continuously instead of relying on periodic checks. In addition, its pre-vetted auditor partner network connects companies with auditors who already understand how Vanta organizes evidence. Therefore, teams spend less time coordinating between audit readiness and final report delivery, while moving through the audit process more efficiently.
Features
- Runs 1,200+ automated hourly control tests across AWS, GCP, Azure, Okta, GitHub, and 375+ integrations
- AI-powered policy builder creates over 30 policies in under two days and links them directly to controls
- Vendor risk management performs continuous reviews and assigns risk scores to third-party vendors
- Automated user access reviews schedule and document approvals for SOC 2 access control requirements
- Supports more than 35 frameworks, including SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, FedRAMP, CCPA, and CJIS
Timeline
- Type I: 2–4 weeks
- Type II: 3–6 months
Pros
- Large integration library connects easily with common cloud and developer tools
- Frequent control testing keeps systems under constant review
- Auditor partner network reduces coordination delays during audits
- Interface works well for non-technical compliance teams
Cons
- Additional features can increase total annual costs
- Usage limits on questionnaires may require plan upgrades
Pricing
• Typically starts around $10,000–$20,000 per year
• Larger deployments can exceed $50,000–$100,000+ annually depending on needs
Best For
Fast-growing SMBs, seed-to-Series B SaaS companies, and teams without a dedicated compliance function that want broad integration coverage and access to experienced audit partners.
3. Drata
Drata often attracts corporate teams and mid-market companies that want strong automation and clear collaboration with auditors. The platform connects with more than 250 tools, and it runs control tests every day, so compliance teams see how their controls perform in real time. In addition, Drata introduces its Audit Hub, which allows engineers and auditors to work together in one shared space. Therefore, teams reduce delays and avoid the long email threads that often slow down audit timelines. At the same time, companies that want faster SOC 2 certification benefit from this direct collaboration and continuous system checks.
Features
- 250+ native integrations across cloud, identity, HRIS, and development tools
- Daily automated control testing across more than 20 supported frameworks
- Audit Hub for direct collaboration between internal teams and auditors
- Editable security policy library with prebuilt templates mapped to SOC 2 controls
- AI-powered control mapping suggestions that guide audit preparation
- Custom controls and separate workspaces for teams managing multiple products or business units
Timeline
- Type I: 1–3 months
- Type II: 6–12 months
Pros
- Strong auditor collaboration tools that reduce delays during audits
- Real-time monitoring keeps teams aware of compliance status at all times
- Reuse of evidence across frameworks helps reduce repeated work
Cons
- Costs can increase as company size and compliance scope expand
- New users may need time to understand the platform due to its depth
- Teams with uncommon tech stacks should confirm integration support before adoption
Pricing
• Starts at about $7,500–$15,000 per year for early-stage startups
• Growing companies may pay $25,000–$45,000+ annually depending on users and frameworks
Best For
Engineering-focused Series A and later companies with complex cloud environments that want compliance to fit directly into existing development workflows.
4. Secureframe
Secureframe organizes more than 200 SOC 2 controls into a clear and practical checklist that first-time compliance owners can follow with confidence. Instead of leaving teams to figure things out alone, the platform combines structured guidance with direct access to in-house compliance experts, many of whom have prior audit experience. In addition, teams receive support when questions come up, which makes the process easier to manage. Therefore, companies move forward with more clarity while still learning how compliance applies to their systems. At the same time, the platform keeps everything organized, so teams avoid confusion as requirements grow.
Features
- Connects with 300+ integrations across cloud providers, HR systems, identity tools, and development platform
- Runs daily automated compliance tests across more than 35 frameworks
- Provides built-in advisory support with access to compliance experts inside the platform
- Includes an automated policy builder with simple templates for faster documentation
- Delivers readiness assessments with gap analysis and clear remediation steps
- Tracks compliance continuously to reduce last-minute audit pressure
- Supports multiple frameworks such as SOC 2, HIPAA, and ISO 27001 within one system.
Timeline
- SOC 2 Type I: typically takes 1–4 months depending on how mature existing controls are
- SOC 2 Type II: usually takes 3–6 months
Pricing
- Starts at approximately $7,500 per year for teams with up to 100 employees
- Pricing increases as headcount grows
- Audit fees are billed separately
Pros
- Clear checklist makes it easier for first-time compliance teams to follow the process
- Access to in-house experts provides guidance throughout the journey
- Strong integration network supports automated evidence collection
- Continuous monitoring helps teams stay prepared instead of rushing before audits
Cons
- Audit fees are not included in platform pricing
- Costs increase as the company grows
- May feel structured for teams that want more flexibility in how they manage controls
Best For
Teams without internal security expertise, companies working toward SOC 2 alongside HIPAA or ISO 27001, and first-time compliance owners who want both software and ongoing guidance.
5. Sprinto
Sprinto stands out as one of the most cost-friendly platforms among SOC 2 providers focused on fast certification. It runs automated compliance tests twice daily, which keeps systems audit-ready at all times. In addition, the platform does more than list tasks; it assigns remediation work directly to the right team members. Therefore, lean teams spend less time coordinating and more time resolving issues. Moreover, this hands-on automation helps companies stay consistent with compliance requirements while reducing delays across departments.
Features
- Runs compliance tests twice daily
- Keeps evidence fresh every 12 hours
- Assigns tasks to the right team members automatically
- Activates pre-built SOC 2 programs quickly
- Supports 200+ integrations (AWS, Azure, GCP, Okta, GitHub, Jira)
- Includes built-in device security monitoring
- Tracks controls at individual resource level
- Auto-assigns fixes when controls fail
- Supports 20+ frameworks (SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS).
Timeline
- SOC 2 Type I: 8–12 weeks
- SOC 2 Type II: 3–6 months (can extend to 12 months).
Pricing
- Typically starts around $4,000–$5,000 per year
- Custom quote required for full pricing.
Pros
- Very affordable for early-stage startups
- Frequent testing keeps compliance up to date
- Reduces manual coordination across teams
- Built-in device monitoring removes extra tool needs
Cons
- Limited flexibility for highly complex environments
- Advanced features may require higher-tier plans
Best For
Budget-conscious startups, international and APAC companies, and cloud-native teams that want their first SOC 2 or ISO 27001 without heavy internal compliance resources.
6. Thoropass
Thoropass stands out among SOC 2 providers for delivering fast certification through a single, integrated platform. It combines compliance automation with audit services, allowing companies to handle evidence collection, control monitoring, remediation, and the final SOC 2 audit without switching vendors. This closed-loop approach reduces delays that typically occur when coordinating between software and auditors. Teams gain clear visibility into progress, while auditors receive verified evidence efficiently, which shortens the path to certification.
Features
- Platform and audit delivered by one vendor
- AI checks evidence for completeness
- Risk management tied to compliance controls
- Dashboard shows percentage-to-audit-ready scores
- In-house auditors and compliance experts included
- Supports SOC 2, SOC 1, ISO 27001, HIPAA, GDPR, CCPA, PCI DSS
- Dedicated compliance manager per account.
Timelines
Type 1: 3–4 months including preparation
Type 2: 6-month observation period on average (can range 3–12 months)
Pros
- Single vendor accelerates end-to-end workflow
- AI identifies gaps before auditor review
- Predictable total spend with no surprise bills
- Real-time readiness score tracks progress
- Strong usability and responsive support
Cons
- Higher upfront cost than platform-only solutions
- Must use in-house auditor network
- Some clients report inconsistent auditor assignment
Pricing
Approximately $10,000–$20,000 per year bundled (platform + audit)
Best For
Companies seeking a concierge-style, single-vendor solution that prioritizes predictable total compliance costs over maximum auditor choice.
8. Scytale
Scytale is an AI-powered compliance platform that combines automation with hands-on support. Each customer receives a dedicated GRC expert from the start, which helps teams without internal security staff move quickly toward SOC 2 certification. In addition, the platform continuously monitors controls and manages evidence, allowing teams to focus on growth while staying audit-ready. Its AI agent flags issues and generates policies, while the integrated auditor partnership keeps the process efficient and coordinated.
Features
- Dedicated GRC expert for every account from day one
- AI agent Scy for risk management, evidence review, and policy creation
- Real-time control monitoring with 24/7 alerts
- Integrated auditor collaboration within the platform
- Support for 30+ frameworks including SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, FedRAMP
- Automated vendor risk management and user access reviews.
Timeline
- Type I: 2–4 weeks
- Type II: 2–4 months
Pricing
- Custom pricing. Estimated $12,000–$18,000/year for startups (platform + audit)
Pros
- Dedicated compliance expert on each account
- Strong cross-framework mapping for global requirements
- AI agent monitors and flags issues around the clock
- Single policy updates apply across all frameworks.
Cons
- Initial setup requires time before automation fully benefits the team
- Some users note minor bugs when submitting large volumes of audit evidence.
Best For
Companies with AWS-heavy infrastructure wanting deep native cloud integrations. Teams without a dedicated compliance officer needing expert hand-holding
9. Scrut Automation
Scrut Automation stands out among SOC 2 providers by helping companies achieve certification quickly. It combines all compliance tasks policy creation, evidence collection, control monitoring, and audit prep into a single interface. This unified approach reduces the delays and confusion that often happen when teams juggle multiple tools. Moreover, the platform continuously monitors systems and surfaces issues early, allowing teams to act before audits begin.
Features
- Single-window dashboard for policies, evidence, controls, auditor communication, and risk management
- Automates over 80% of evidence collection across 80+ cloud, identity, and HR integrations
- 100+ prebuilt policy templates, framework-mapped and editable in-platform
- Real-time control monitoring with configurable alerts for failures and threshold breaches
Timeline
- Type I: 3–6 months
- Type II: 6–12 months
Pricing
- Custom pricing
- Contact sales for details
Pros
- High automation of evidence collection
- Large library of expert-built, editable policy templates
- Unified platform reduces tool sprawl
- No extra fees for core compliance features
Cons
- Platform may feel complex for small, first-time teams
- Some enterprise features lag behind larger competitors.
Best For
Mid-market and growth-stage companies that want enterprise-depth GRC without enterprise pricing, managed from a single hub across multiple frameworks.
10. Prescient Security
Prescient Security is a globally recognized audit and penetration testing firm. It holds AICPA accreditation and CREST certification, which makes it one of the most credible pure-play SOC 2 audit firms for companies seeking fast certification. The firm uses a risk-based approach, customizing each engagement to match the client’s actual risk profile. This method accelerates audit timelines and helps organizations avoid unnecessary compliance costs while focusing on controls that truly matter.