

If you run a cloud hosting business, whether you offer managed hosting, VPS, dedicated servers, or full IaaS, choosing the right SOC 2 firms for cloud hosting providers is no longer optional. A SOC 2 report has become a procurement requirement. Enterprise customers no longer rely on promises that your backups run as scheduled, access controls work, or your data center uses secure entry systems. They expect an independent CPA firm’s attestation before they sign a contract.
Choosing a SOC 2 firm for a cloud hosting provider differs from choosing one for a typical SaaS company. Hosting providers manage physical infrastructure controls, including data center access, environmental monitoring, and hardware disposal. They must also maintain the logical security controls every cloud business needs. Many providers support customers who use their SOC 2 reports to satisfy their own compliance requirements.
Your auditor should understand multi-tenant infrastructure and subservice organizations, including colocation facilities, upstream cloud providers, and DDoS mitigation vendors. They should also know how your availability controls support your SLAs. Choose the wrong firm, and you’ll end up with a report that fits a 12-person SaaS startup instead of a cloud hosting platform operating across multiple regions.
Why Cloud Hosting Providers Need SOC 2
A hosting provider’s reputation depends on one promise: your customers’ data, workloads, and uptime are secure. A SOC 2 report validates that promise through an independent audit. For cloud hosting providers, it has become a business requirement for three reasons.
First, enterprise customers expect a current SOC 2 Type II report during vendor security reviews. Without one, you’ll spend time completing lengthy security questionnaires for every potential customer.
Second, hosting providers operate multi-tenant environments where a single security gap can affect multiple customers. SOC 2 evaluates the controls that reduce these risks, including access management, network security, encryption, and incident response.
Finally, SOC 2 gives you a competitive advantage. A clean Type II report builds trust, shortens procurement cycles, and helps you win enterprise and regulated customers. It also demonstrates that your infrastructure, physical security, and operational controls meet recognized security standards.
The Top 12 SOC 2 Firms for Cloud Hosting Providers
1. A-LIGN
A-LIGN is one of the most experienced SOC 2 Firms for Cloud Hosting Providers. It has completed thousands of SOC 2 audits and works with organizations that need multiple compliance frameworks. If you plan to pursue SOC 2 now and add standards like FedRAMP, HITRUST, or PCI DSS later, A-LIGN can manage them under one engagement. Its A-SCEND platform also helps you reuse audit evidence across frameworks, reducing duplicate work and speeding up future audits.
Features
- A-SCEND platform for managing audits and compliance evidence.
- EvidenceIQ AI to review and organize audit evidence.
- Cross-framework evidence reuse to reduce duplicate documentation.
- Supports SOC 1, SOC 2, SOC 3, ISO 27001, PCI DSS, HIPAA, HITRUST, CMMC, and FedRAMP.
- Experienced with infrastructure-heavy environments, including managed hosting and IaaS providers.
- Dedicated audit teams with expertise across multiple compliance frameworks.
Pros
- Extensive experience auditing cloud hosting and infrastructure companies.
- Makes it easier to expand into additional compliance frameworks.
- Reuses existing evidence, saving time during future audits.
- Strong reputation with enterprise procurement and security teams.
- Large team helps keep complex engagements on schedule.
Cons
- Costs more than many boutique SOC 2 firms.
- Large engagements may feel less personalized.
- Sales and onboarding can take longer than with smaller firms.
Pricing
Custom pricing. Most mid-market cloud hosting providers can expect SOC 2 Type II audits to start around $25,000, with costs increasing for larger environments or multi-framework engagements.
Best For
Managed hosting providers, VPS companies, dedicated server providers, and IaaS businesses that expect to add frameworks like FedRAMP, HITRUST, or PCI DSS as they grow.
Verdict
A-LIGN is one of the strongest choices for growing infrastructure companies. It combines deep audit experience with broad compliance expertise, making it ideal for providers that view SOC 2 as the first step in a long-term compliance strategy.
2. Schellman & Company
Schellman specializes in IT attestation and compliance audits. It works with cloud-native companies that need both SOC 2 and ISO 27001 certifications. The firm uses a single-assessor model, allowing one team to handle multiple frameworks during the same engagement. This approach reduces duplicated work and keeps audits consistent across cloud environments.
Features
- Combined SOC 2 and ISO 27001 assessments.
- Secure Portal for evidence collection and audit management.
- More than 2,000 SOC reports issued annually.
- PCAOB-registered CPA firm.
- FedRAMP 3PAO assessment services.
- Experience with AWS, Azure, GCP, and multi-cloud environments.
Pros
- Strong expertise in cloud infrastructure audits.
- Supports multiple frameworks under one engagement.
- Fixed-fee pricing improves budget predictability.
- Technical audit teams understand complex hosting environments.
Cons
- Audit schedules often book months in advance.
- Less flexibility for urgent engagements.
- Premium pricing for larger environments.
Pricing
Custom pricing. SOC 2 Type I engagements typically range from $25,000–$45,000. Type II audits generally range from $35,000–$75,000, depending on scope.
Best For
Cloud hosting providers running multi-cloud or multi-region infrastructure that need SOC 2 and ISO 27001 from the same auditor.
Verdict
Schellman stands out for its technical expertise and cloud focus. It is an excellent choice for mature hosting providers that need multiple compliance frameworks under one audit partner.
3. BARR Advisory
BARR Advisory focuses almost exclusively on cloud-based organizations. Its auditors work with modern cloud environments every day, making the firm a strong fit for hosting providers that operate entirely on AWS, Azure, or Google Cloud. It also offers security testing alongside compliance services.
Features
- SOC 1, SOC 2, SOC 3, and SOC for Cybersecurity audits.
- ISO 27001 certification services.
- HIPAA and HITRUST assessments.
- Penetration testing and vulnerability assessments.
- Fixed-fee pricing.
- Cloud-first audit methodology.
Pros
- Strong cloud infrastructure expertise.
- Senior auditors stay involved throughout the engagement.
- Combines compliance and security testing.
- Good fit for healthcare and fintech hosting providers.
Cons
- Smaller team than larger national firms.
- Less recognizable brand outside the technology sector.
- Limited capacity for very large engagements.
Pricing
Custom pricing. Contact BARR Advisory for a quote.
Best For
Cloud-native hosting providers that also need HIPAA, HITRUST, or security testing.
Verdict
BARR Advisory offers a hands-on experience that many growing hosting providers value. It works best for cloud-first businesses that want close collaboration throughout the audit.
4. Coalfire
Coalfire combines SOC 2 auditing with a broad cybersecurity practice. It has extensive experience helping cloud service providers meet commercial, federal, and payment security requirements. The firm also ranks among the leading FedRAMP assessment organizations.
Features
- Combined SOC 2 and FedRAMP assessment services.
- PCI DSS Qualified Security Assessor (QSA) services.
- More than 600 framework specialists.
- Over 500 SOC reports issued annually.
- Large cybersecurity consulting practice.
Pros
- Strong experience with government and regulated industries.
- Supports complex compliance programs.
- Large technical team handles enterprise environments.
- Deep expertise in cloud infrastructure.
Cons
- Higher pricing than many boutique firms.
- Large engagements may feel less personalized.
- Better suited for complex environments than simple SOC 2 audits.
Pricing
Custom pricing. Contact Coalfire for a quote.
Best For
Hosting providers pursuing FedRAMP, PCI DSS, or government contracts alongside SOC 2.
Verdict
Coalfire delivers the most value when SOC 2 is only one part of a larger compliance roadmap. Smaller hosting providers may find more affordable alternatives.
5. Prescient Security
Prescient Security combines SOC 2 audits with application security testing. The firm also integrates closely with compliance platforms like Vanta, Drata, and Trustero. Its remote-first approach simplifies the audit process for distributed engineering teams.
Features
- Remote SOC 2 audits with Slack-based communication.
- Native integrations with Vanta, Drata, and Trustero.
- Penetration testing services.
- Support for more than 25 compliance frameworks.
- CREST accreditation.
- Cloud Security Alliance STAR Auditor status.
Pros
- Competitive pricing.
- Fast and fully remote audit process.
- Strong integration with leading compliance platforms.
- Combines auditing and penetration testing.
Cons
- Smaller brand than larger audit firms.
- Type II engagements can take longer than Type I.
- Some enterprise buyers prefer larger firms.
Pricing
SOC 2 Type II audits typically range from $7,000–$30,000.
Best For
Cloud-native hosting startups and growth-stage providers already using Vanta or similar compliance platforms.
Verdict
Prescient Security delivers strong value for startups and growing infrastructure companies. Its remote-first model keeps audits efficient without sacrificing quality.
6. Johanson Group LLP
Johanson Group is a boutique CPA firm known for fast SOC 2 engagements. It focuses on helping companies achieve their first SOC 2 report quickly while keeping costs predictable. Partners remain directly involved throughout the engagement.
Features
- SOC 1, SOC 2, SOC 3, ISO 27001, and HIPAA audits.
- Fast Type I audit turnaround.
- Fixed-fee pricing.
- Direct partner involvement.
- Streamlined three-step audit process.
Pros
- One of the fastest paths to a first SOC 2 report.
- Predictable pricing.
- Personalized service.
- Well suited to small engineering teams.
Cons
- Smaller team than national firms.
- Limited FedRAMP expertise.
- Lower brand recognition with enterprise procurement teams.
Pricing
SOC 2 Type I audits typically start around $15,000.
Best For
Early-stage hosting providers, VPS companies, and startups that need a SOC 2 report quickly.
Verdict
Johanson Group is an excellent option for companies pursuing their first SOC 2 audit. It prioritizes speed, affordability, and personalized service over broad compliance capabilities.
7. Linford & Company
Linford & Company specializes in SOC and IT attestation services. The firm stands out for its expertise in both SOC 1 and SOC 2 audits. That makes it a strong choice for hosting providers with usage-based billing, provisioning systems, or financial reporting requirements.
Features
- Combined SOC 1 and SOC 2 audit expertise.
- More than a decade of IT attestation experience.
- Experienced team focused on cloud infrastructure.
- Startup-friendly engagement structure.
- Budget-conscious audit approach.
Pros
- Strong choice for providers that need both SOC 1 and SOC 2.
- Understands cloud infrastructure and financial controls.
- Works well with startups and smaller businesses.
- Flexible engagement model for growing companies.
Cons
- Smaller team than national audit firms.
- Longer wait times during busy audit seasons.
- Lower brand recognition outside the compliance industry.
Pricing
Custom pricing. Engagement costs generally fall within the lower to mid-range for specialist SOC 2 firms.
Best For
Hosting providers with usage-based billing or financial reporting systems that need both SOC 1 and SOC 2 audits.
Verdict
Linford & Company delivers the most value for infrastructure businesses that need financial control audits alongside SOC 2. If SOC 1 is not part of your roadmap, other firms may offer broader compliance expertise.
8. Thoropass
Thoropass combines compliance software and auditing under one provider. Unlike most platforms, it owns an in-house CPA firm that performs the audit. This setup removes the need to coordinate between a compliance platform and an external auditor.
Features
- Compliance platform with an integrated CPA audit team.
- AI-powered evidence review using First Pass AI and Smart Sort AI.
- Supports SOC 1, SOC 2, ISO 27001, ISO 42001, HIPAA, HITRUST, GDPR, PCI DSS, and CMMC.
- More than 100 integrations, including AWS, Okta, and GitHub.
- CREST-accredited security services.
Pros
- One vendor manages both compliance and auditing.
- AI speeds up evidence collection and review.
- Reduces coordination between multiple providers.
- May lower overall compliance costs.
Cons
- Switching auditors requires leaving the platform.
- Fewer integrations than Vanta.
- Smaller customer base than leading compliance platforms.
Pricing
Platform pricing starts around $8,700 per year. Bundled platform and audit packages can exceed $80,000 per year, depending on scope.
Best For
Growth-stage hosting providers that want one vendor for compliance automation and SOC 2 auditing.
Verdict
Thoropass simplifies the compliance process by combining software and auditing. It works best for companies that value convenience over auditor flexibility.
9. Vanta
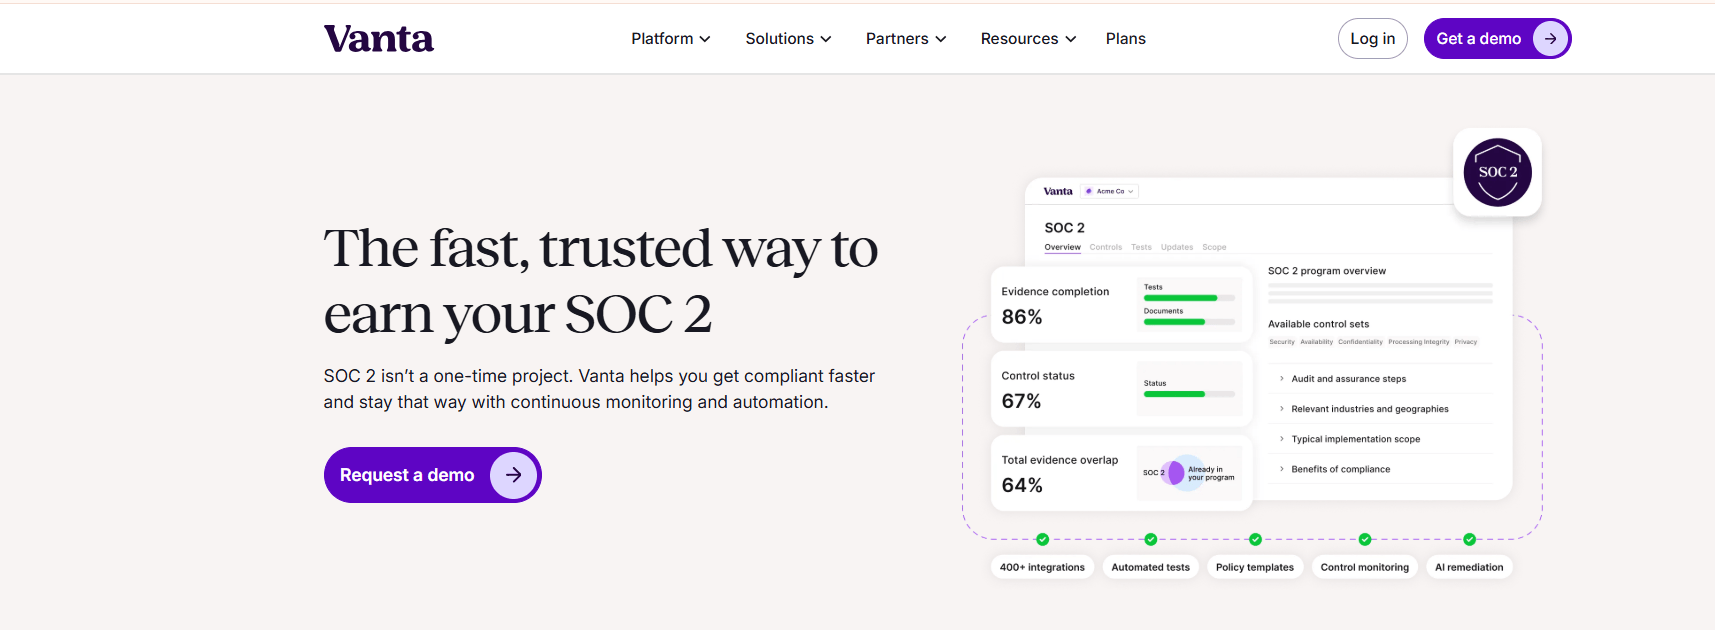 Vanta is the largest compliance automation platform on the market. It automates evidence collection across cloud environments and helps organizations prepare for SOC 2 faster. While it simplifies audit readiness, it does not perform audits. You’ll still need to hire a CPA firm.
Features
- Automated evidence collection across 35+ frameworks.
- Native integrations with AWS, Azure, GCP, Okta, GitHub, and more.
- Continuous control monitoring.
- Customer-facing Trust Center.
- Large auditor partner network.
- AI-assisted compliance monitoring.
Pros
- Extensive integration library.
- Automates much of the audit preparation process.
- Widely supported by SOC 2 auditors.
- Significantly reduces manual evidence collection.
Cons
- Requires an endpoint agent on employee devices.
- Support quality varies across pricing tiers.
- Renewal costs can increase over time.
- Does not perform the audit itself.
Pricing
Custom pricing. Plans typically start around $7,500 per year. CPA audit fees are separate.
Best For
Cloud-native hosting providers preparing for their first SOC 2 or ISO 27001 certification.
Verdict
Vanta remains one of the strongest compliance automation platforms available. Its broad integrations and auditor ecosystem make it an easy choice for most cloud hosting providers.
10. Drata
Drata focuses on continuous compliance monitoring and automation. The platform also receives consistently high ratings for customer support. It helps hosting providers monitor controls in real time instead of preparing only when an audit approaches.
Features
- Continuous monitoring for security controls.
- Multi-framework support with shared controls.
- Integrations with AWS, GitHub, Okta, and Google Workspace.
- AI-powered vendor risk management.
- Built-in Trust Center.
Pros
- Excellent customer support.
Strong real-time compliance monitoring.
Simplifies collaboration with auditors.
Reduces duplicate work across multiple frameworks.
Cons
- Less effective for highly customized infrastructure.
- Additional integrations may increase costs.
- Audit services require a separate CPA firm.
Pricing
Plans generally start between $7,500 and $15,000 per year. Custom integrations may cost extra.
Best For
Cloud-native hosting providers that want continuous compliance monitoring and responsive customer support.
Verdict
Drata is an excellent platform for companies that need ongoing compliance visibility. It performs best in standard cloud environments with minimal custom infrastructure.
11. Secureframe
Secureframe combines compliance automation with hands-on support. It also offers dedicated features for companies pursuing federal compliance standards like CMMC. Its cross-framework mapping reduces duplicate work across multiple certifications.
Features
- More than 300 cloud integrations.
- AI-powered policy drafting and evidence validation.
- Continuous compliance monitoring.
- Cross-framework control mapping.
- Dedicated compliance experts across all plans.
Pros
- Responsive support across every pricing tier.
- Strong multi-framework automation.
- Excellent choice for federal compliance programs.
- Reduces duplicate evidence collection.
Cons
- Smaller customer base than Vanta or Drata.
- Higher starting price than some competitors.
- Audit services require a separate CPA firm.
Pricing
Plans start around $7,500 per year. Pricing varies based on team size and compliance frameworks.
Best For
Hosting providers planning to pursue SOC 2, ISO 27001, CMMC, or other federal compliance standards.
Verdict
Secureframe balances strong automation with personalized support. It is a smart choice for infrastructure providers with long-term compliance goals.
12. Sprinto
Sprinto offers one of the most affordable compliance automation platforms for growing businesses. Despite its lower entry price, it includes features that many competitors reserve for premium plans. The platform also performs well for globally distributed teams.
Features
- More than 300 integrations.
- Continuous compliance monitoring.
- Sprinto AI for automated compliance tasks.
- Multi-framework support from one dashboard.
- Built-in Trust Center and policy management.
Pros
- Competitive pricing.
- Strong feature set at the entry level.
- Responsive customer support.
- Good fit for distributed engineering teams.
Cons
- Requires an endpoint agent.
- Some cloud configurations require manual adjustments.
- Costs increase as organizations add entities or integrations.
- CPA audit services are not included.
Pricing
Plans typically start between $8,000 and $10,000 per year. Larger deployments can exceed $20,000 annually. CPA audit fees are separate.
Best For
Budget-conscious cloud hosting providers that want robust compliance automation without paying enterprise prices.
Verdict
Sprinto offers one of the best price-to-feature ratios in the market. It is a strong option for startups and growing hosting providers that need automation without unnecessary complexity.
Conclusion
Choosing the right SOC 2 Firms for Cloud Hosting Providers depends on your infrastructure, compliance goals, and growth plans. Ultimately, choose a firm with proven experience auditing cloud infrastructure. Your auditor should understand multi-tenant environments, cloud platforms, physical infrastructure controls, and the challenges unique to hosting providers. The right partner won’t just help you pass an audit. They’ll help you build trust with enterprise customers and support your long-term compliance strategy.